
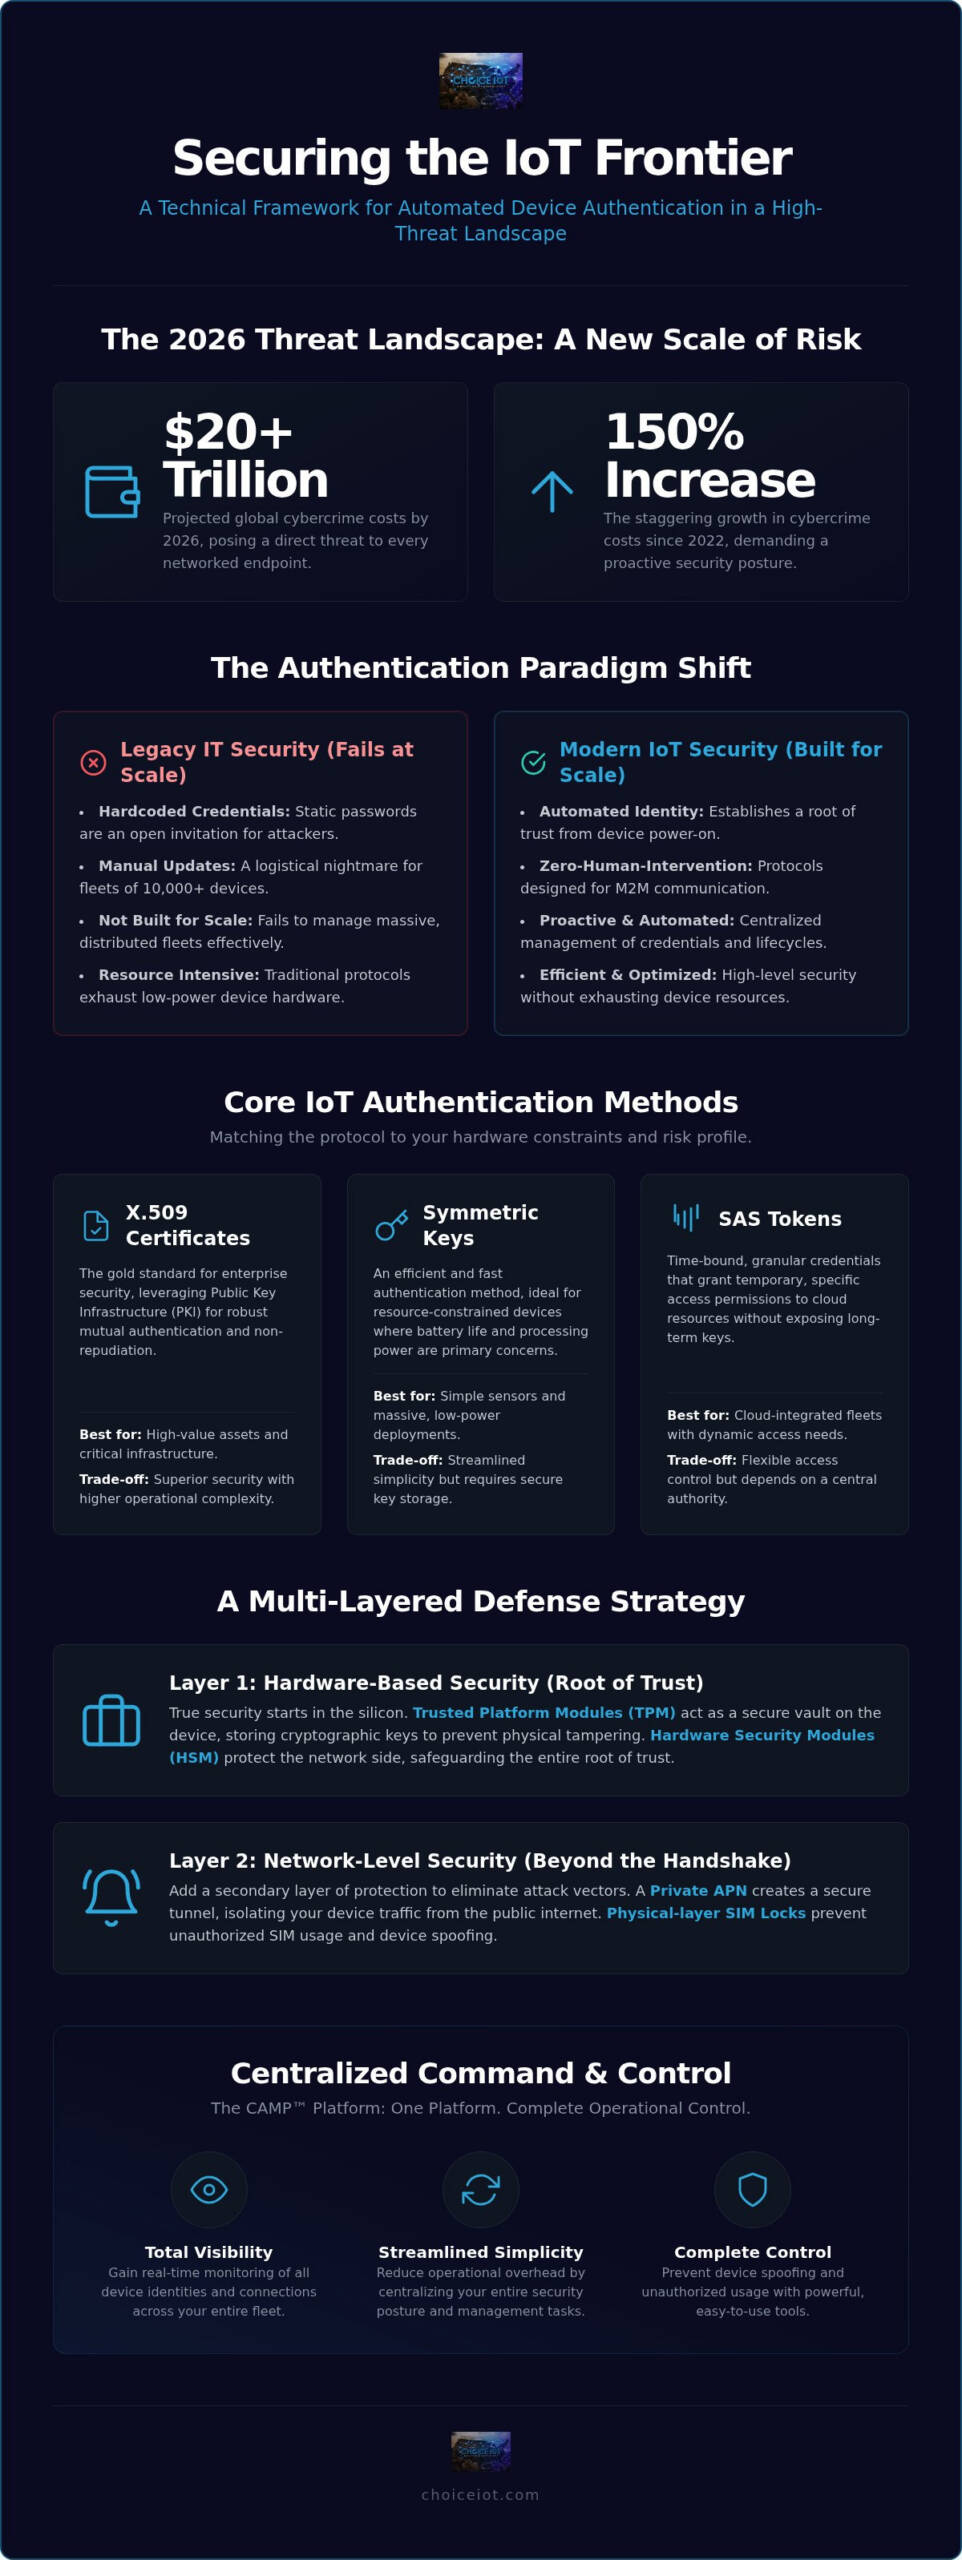
Global cybercrime costs are projected to exceed $20 trillion by the end of 2026, representing a 150% increase since 2022. For enterprise leaders, this isn’t just a data point. It’s a direct threat to every networked endpoint in your fleet. Managing thousands of unique device identities while balancing low-power constraints often feels like a losing battle against complexity. You know that scaling shouldn’t mean compromising your perimeter. It’s time to simplify.
Mastering iot network security best practices requires a shift from reactive patching to proactive, automated authentication. This guide provides the technical framework needed to secure your deployment from the device edge to the network core. We’ll examine how to eliminate unauthorized SIM usage through physical-layer locks and secure data tunnels like a Private APN. You will learn to use the CAMP™ platform to centralize your security posture, reducing operational overhead while preventing device spoofing. Total visibility. Streamlined simplicity. Complete operational control starts here.
Key Takeaways
- Understand why IoT authentication requires zero-human-intervention protocols to maintain security across massive, distributed fleets.
- Evaluate the technical trade-offs between certificates, tokens, and symmetric keys to find the right fit for your hardware constraints.
- Implement iot network security best practices by aligning your authentication strategy with the specific risk profile of your deployment.
- Learn how to add a secondary layer of protection using physical-layer SIM Lock and Private APN tunnels to prevent device spoofing.
- Discover how to centralize operational control through the CAMP™ platform for real-time visibility and reduced management overhead.
Understanding IoT Device Authentication: The Digital Gatekeeper
Authentication is the automated verification of a device’s right to access your network. It’s the digital handshake. In the machine-to-machine (M2M) world, this process happens without human intervention. Implementing iot network security best practices starts with this identity layer. If a device cannot prove its legitimacy, it’s a threat. Pure and simple. We’ve moved past simple passwords. Modern deployments require sophisticated, identity-driven security to survive in the 2026 connected ecosystem. This is about establishing a root of trust from the moment a device powers on.
Why Traditional Authentication Fails for IoT
Legacy IT security models aren’t built for scale. Hardcoded credentials and default passwords are an open invitation for attackers. When your fleet grows to 10,000 devices, manual updates are a logistical nightmare. You need automated systems that handle credential rotation and lifecycle management. Resource constraints also play a major role. Many devices have limited processing power and battery life. Standard authentication protocols must be optimized. They need to provide high-level security without exhausting the device’s hardware. Efficiency is non-negotiable. Without this balance, security becomes a bottleneck for performance.
The Role of Identity in 2026 IoT Ecosystems
Identity is the foundation of trust. By 2026, verified device identity is essential for regulatory compliance and data integrity. It’s how you prevent man-in-the-middle (MITM) attacks from compromising your network core. If the identity is verified, the data is trusted. The emergence of 5G Redcap adds another layer of complexity. These mid-tier devices need robust authentication that fits their specific performance profile. A secure identity ensures that only authorized hardware communicates, which is a cornerstone of iot network security best practices. Using a centralized hub like the CAMP™ platform allows for real-time monitoring of these identities. It provides One Platform. Complete Operational Control. This keeps your operations streamlined, protected, and fully under your control.
Core IoT Authentication Methods: Certificates, Tokens, and Keys
Authentication isn’t a one-size-fits-all solution. Your choice of protocol defines your defensive perimeter. For low-power, massive deployments, Symmetric Key authentication remains a staple. It’s efficient. It’s fast. However, it requires secure key storage on both the device and the server. For cloud-integrated fleets, Shared Access Signatures (SAS) tokens offer a time-bound alternative. These tokens grant granular access without exposing long-term credentials. Adhering to iot network security best practices means matching the method to the hardware’s processing capability and the data’s sensitivity.
X.509 Certificates vs. Symmetric Keys
X.509 Digital Certificates represent the gold standard for enterprise-grade security. They leverage Public Key Infrastructure (PKI) to provide superior non-repudiation and mutual authentication. The device and the network both prove their identity. While robust, certificates introduce operational complexity. Lifecycle management, including renewal and revocation, requires significant back-end automation. Symmetric keys offer streamlined simplicity but lack the cryptographic depth of PKI. Choose certificates for high-value assets. Use keys for simple sensors where battery life is the primary constraint. Following guidelines from the OWASP IoT Project helps ensure your chosen method meets modern standards.
Hardware-Based Authentication: TPM and HSM
True security starts in the silicon. Trusted Platform Modules (TPM) act as a secure element on the device board. They store cryptographic keys in a way that prevents physical tampering. Hardware Security Modules (HSM) extend this protection to the network side, safeguarding the root of trust. This hardware-level identity becomes even more powerful when paired with network-level controls. Integrating hardware-level identity with a private APN for IoT creates a multi-layered barrier. It isolates your traffic from the public internet entirely. This holistic approach is central to iot network security best practices in 2026. For real-time visibility into these connections, managing your fleet through a centralized hub like the CAMP™ platform ensures you maintain total control. It’s the most effective way to secure your connectivity across multiple carriers without increasing operational friction.
Strategic Deployment: Choosing the Right Method for Your Scale
Security isn’t just a technical hurdle. It’s a strategic investment. Every device added to your fleet represents a potential entry point for attackers. Scaling requires a disciplined framework. You must align your authentication method with the device’s value and its specific risk profile. High-value assets demand the rigors of PKI. Simple sensors might thrive with symmetric keys. Adopting iot network security best practices means acknowledging that over-securing low-risk devices can be as costly as under-securing critical infrastructure. Balance is the priority.
The Decision Matrix: Cost, Security, and Power
Quantifying the cost of a security breach is the first step. A single compromised endpoint can lead to millions in losses. However, the management overhead of a complex PKI infrastructure is also significant. You have to account for the total cost of ownership. For 5G Redcap devices, power-saving modes are critical. Heavy cryptographic handshakes can drain batteries prematurely, shortening the field life of your hardware. The optimal balance for industrial deployments is achieved when cryptographic strength matches the hardware’s operational lifespan without inducing battery depletion. Efficiency drives profitability.
Automating Provisioning for Large-Scale Fleets
Manual intervention is the enemy of scale. For VARs and integrators, managing multi-carrier deployments requires a streamlined approach. Zero-touch provisioning is the goal. You need the ability to ship hardware directly to the site and have it authenticate automatically upon power-up. This reduces expensive “truck rolls” and minimizes human error. Managing these logistics across different carriers becomes simple when using a centralized IoT connectivity management platform. Centralization provides the visibility needed to monitor authentication health in real-time. It allows for remote resets and secure credential updates without physical access. To secure your next deployment with total operational control, partner with Choice IoT for a scalable connectivity solution.
Beyond the Handshake: Network-Level Security with Choice IoT
Software handshakes are only half the battle. True security requires a hardened network layer. Choice IoT moves iot network security best practices beyond the device edge by integrating authentication with network-level operational control. Through the CAMP™ platform, you gain a secondary layer of defense that software-only solutions ignore. One Platform. Complete Operational Control. This is the foundation of a resilient deployment. It’s about removing friction while maximizing protection.
Isolating your traffic is essential. By utilizing a Private APN, Choice IoT creates a secure tunnel that keeps authentication traffic entirely off the public internet. This prevents external actors from even seeing your devices. It’s invisible security. You can’t attack what you can’t find. This network-level isolation ensures that your M2M handshakes remain private, protected, and reliable.
Operational Control with CAMP™
Visibility is power. The CAMP™ platform provides real-time monitoring for every SIM in your fleet from a single, centralized dashboard. You don’t just see connections; you control them. Use the platform to set intelligent alerts based on specific data-usage thresholds. This allows you to identify compromised devices before they become significant liabilities. If a device behaves erratically or exceeds its profile, use Remote Network Reset to restore connectivity or isolate the unit. No on-site visits required. It’s rapid. It’s efficient. It’s total control at your fingertips.
Locking Down the Edge: SIM and Device Binding
Physical security matters as much as digital protocols. Choice IoT’s SIM Lock feature binds the SIM identity to specific hardware. This effectively prevents unauthorized SIM swaps and device spoofing. Even if an attacker gains physical access to a device, the SIM is useless in any other hardware. Utilizing multi-carrier IoT SIM cards ensures these security policies remain consistent and active as your devices move across global borders. Secure connectivity, everywhere.
Integration is seamless. Our robust API allows you to push security alerts directly into your existing CRM or ERP systems. Automate your response. Eliminate the logistical stress of manual monitoring. By combining hardware-level binding with network-wide visibility, you establish a security posture that is inherently robust and ready to scale. This is the Choice IoT promise: streamlined simplicity and total reliability for your entire ecosystem.
Future-Proof Your IoT Infrastructure
Securing a massive device fleet requires more than just a digital handshake. It demands a strategy that synchronizes robust authentication with network-level operational control. By 2026, the complexity of managing thousands of identities will only increase. You need a framework that balances cryptographic strength with real-world hardware constraints. Adopting iot network security best practices ensures your deployment remains resilient against spoofing and unauthorized access. Total visibility. Zero friction. Complete reliability.
Choice IoT provides the tools to simplify this technical landscape. Leverage CAMP™ for real-time visibility across your entire fleet. Rapid deployment. Invisible security. Utilize Private APN security to isolate your traffic from the public internet. Implement SIM Lock and device change alerts to anchor your security at the physical layer. This isn’t just about defense. It is about empowering your growth through streamlined simplicity and total control. You have the vision. We have the foundation. Build with the confidence of a partner that has already solved the industry’s most complex hurdles.
Get One Platform and Complete Operational Control with Choice IoT today. Secure your connectivity from the device edge to the network core.
Frequently Asked Questions
What is the difference between IoT authentication and authorization?
Authentication confirms a device’s identity; authorization defines its access rights. Think of authentication as the badge that gets a device through the door. Authorization is the set of permissions that determines which rooms it can enter. In complex IoT ecosystems, you need both to ensure that even a verified device can’t access sensitive network cores without specific clearance. This dual-layered approach is essential for maintaining total operational control.
Is X.509 the best authentication method for all IoT devices?
X.509 isn’t always the right choice. While it offers superior security through Public Key Infrastructure (PKI), the computational overhead can be too heavy for low-power sensors. Implementing iot network security best practices means choosing the most robust method your hardware can handle without draining the battery. For mid-tier devices like 5G Redcap, X.509 provides excellent protection, but simpler sensors often require more efficient symmetric key models.
How do symmetric keys work in IoT authentication?
Symmetric key authentication uses a single secret key shared between the device and the server. The device proves its identity by encrypting a challenge sent by the server. It’s fast. It’s efficient. It’s perfect for high-volume, low-power deployments where processing resources are limited. However, you must ensure the keys are stored securely on the hardware to prevent a single point of failure from compromising your entire fleet.
Can I use a Private APN to improve device authentication security?
A Private APN significantly enhances security by isolating authentication traffic from the public internet. It creates a secure, private tunnel for your data. This prevents external hackers from seeing your devices or intercepting authentication handshakes. Integrating this network-level isolation with your device-level protocols is a cornerstone of iot network security best practices. It ensures that your internal communications remain invisible and protected from outside threats.
What happens if an IoT device fails authentication?
If a device fails authentication, the system must immediately block its access to the network. This isn’t just about denial; it’s about visibility. On the CAMP™ platform, authentication failures trigger real-time alerts. This allows your team to investigate whether the failure was a technical glitch or a malicious spoofing attempt. Rapid isolation prevents potential threats from spreading, keeping your core infrastructure secure and your operations running smoothly.
How does SIM Lock serve as a security measure for IoT devices?
SIM Lock acts as a physical-layer security barrier by binding a SIM card to a specific device’s IMEI. If an unauthorized user tries to swap the SIM into a different modem, the connection is instantly rejected. This prevents SIM theft and unauthorized data usage. It’s a simple, powerful way to ensure that your connectivity remains exclusive to your trusted hardware, providing an extra layer of protection beyond digital certificates.