By the end of 2026, relying on the public internet for enterprise IoT isn’t just a security risk; it’s a compliance liability. With the EU Cyber Resilience Act enforcement beginning in September, the margin for error has disappeared. You likely feel the weight of managing a sprawling device fleet with limited visibility. Data breaches via the public web are a constant threat. Complex IP management for M2M communication shouldn’t be your daily reality. It’s time for a more robust architecture. Implementing a private apn for iot is the definitive move to secure your perimeter and protect your infrastructure.
You deserve a network that works as hard as your hardware. We agree that fragmented security and costly truck rolls for simple resets are relics of the past. This guide provides the strategic blueprint to eliminate public internet exposure and gain total operational control over your deployment. You’ll learn to leverage static IPs for simplified communication and use the CAMP™ platform for real-time visibility. We’ll cover everything from 5G Redcap integration to automated SIM locking. Secure connectivity. Centralized management. Absolute reliability. Let’s build your private pathway.
Key Takeaways
- Secure your perimeter. Master the essentials of a private apn for iot to bypass public internet threats and satisfy 2026 compliance standards.
- Optimize data routing. Establish direct pathways from devices to your private cloud or data center using VPN and MPLS tunnels.
- Simplify deployments. Hardcode configurations into hardware to ensure carrier-agnostic security across all global deployments.
- Centralize management. Use the CAMP™ platform for real-time traffic monitoring; leverage remote network resets to eliminate expensive truck rolls.
- Future-proof your fleet. Integrate 5G Redcap for high-performance, cost-effective connectivity that scales with your operational needs.
What is a Private APN and Why Does IoT Security Depend on It?
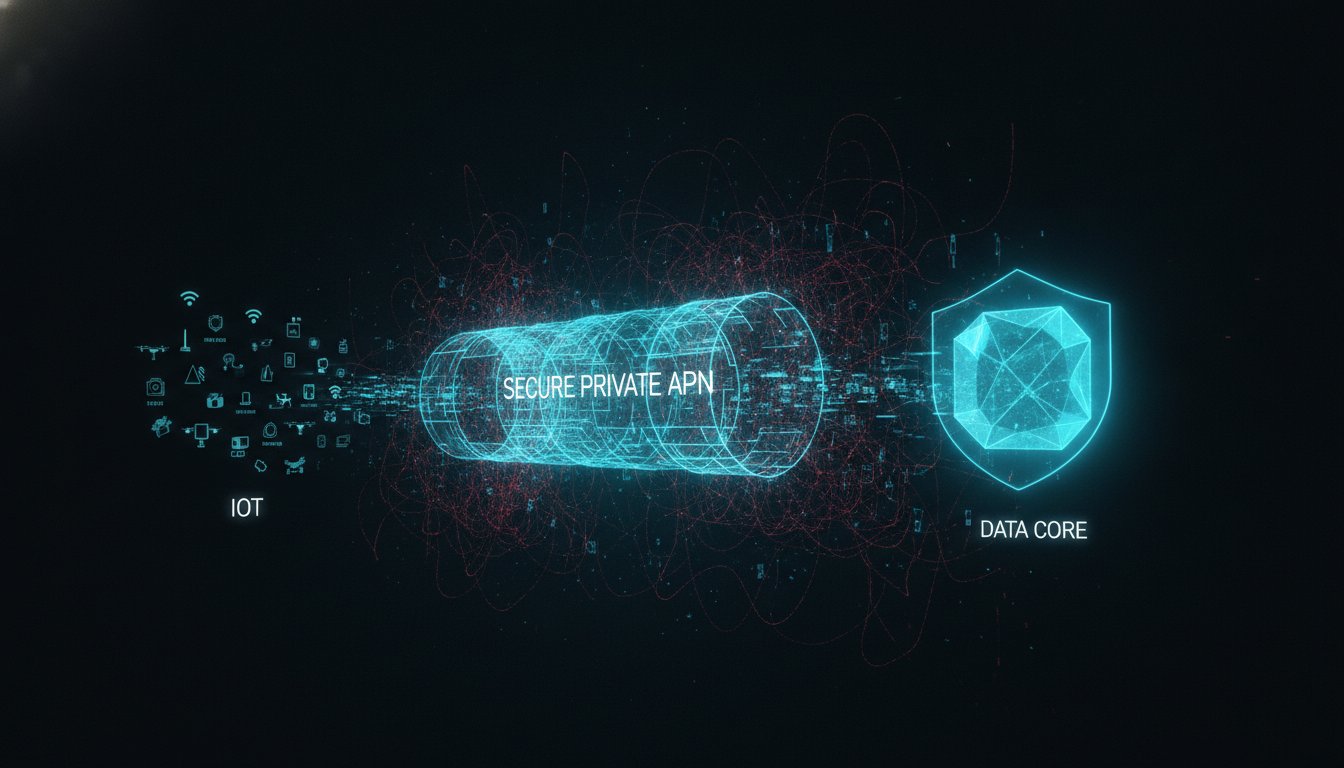
A Private APN (Access Point Name) acts as a dedicated gateway between a cellular network and your private infrastructure. It’s the essential foundation for secure machine-to-machine (M2M) ecosystems. While standard connectivity relies on the public internet, a private apn for iot creates a secure, point-to-point tunnel. This pathway ensures your data never touches the World Wide Web. It provides a level of isolation that standard consumer-grade connections simply cannot match. In modern deployments, this isn’t just an option; it’s a requirement for operational integrity.
Private APN vs. Public APN: The Critical Differences
Public APNs are the default for consumer mobile plans. They use dynamic IPs and shared bandwidth. This environment is a playground for attackers. Devices on public APNs are visible to the entire internet, making them vulnerable to automated scanning and brute-force attacks. In fact, using “Public” defaults is the #1 cause of IoT data breaches today. This “Shadow IoT” risk grows exponentially as your fleet scales.
Private APNs offer a different reality. You gain total control. Key advantages include:
- Static IP support for consistent, predictable device reaching and simplified management.
- Isolated traffic that stays entirely off the public grid.
- Custom routing rules tailored to your specific data center or cloud VPC.
How Private APN Architecture Eliminates Public Exposure
Network-level isolation is the core benefit. By establishing a private apn for iot, you stop threats before they ever reach the device. This architecture bypasses the public packet core entirely. The result is lower latency and significantly higher reliability for mission-critical applications. It removes the device from the reach of external pings and unauthorized access attempts, effectively making your hardware invisible to the public web.
This setup integrates perfectly with sophisticated static ip vs dynamic ip strategies. Instead of managing a chaotic pool of changing addresses, you gain a structured environment. You control the gateway. You control the traffic. You eliminate the vulnerability. This is the first step toward building a zero-trust IoT environment that scales without increasing your attack surface or administrative overhead.
The Technical Architecture of Secure IoT Data Transmission
Understanding the flow of data within a private apn for iot is essential for maintaining a hardened perimeter. The process begins at the device level. When a module initiates a connection, it requests access using a specific APN string hardcoded into the hardware. The carrier network identifies this request and routes it to a private gateway rather than the public internet. Authentication occurs via a RADIUS server or a similar secure protocol, ensuring only authorized SIMs enter the environment. Once the session is established, data moves through an encrypted tunnel, such as a VPN or MPLS, directly to your cloud VPC or on-site data center. Secure. Direct. Invisible.
Scalability is a primary driver for this architecture. A single private gateway can manage thousands of devices under one secure umbrella. This centralization simplifies policy enforcement. Instead of configuring security rules for every individual endpoint, you manage the gateway. Redundancy is equally critical. By utilizing multi-carrier configurations, your deployment maintains uptime even if a specific carrier core experiences a localized outage. Your data remains in transit, protected by the same private protocols across different networks.
Static IPs and M2M Communication
Effective machine-to-machine (M2M) communication often requires the ability to reach into a device remotely for polling or updates. Achieving a secure static ip for m2m is nearly impossible on public networks without exposing the device to constant scanning. Within a private APN, static IPs provide a fixed, known address for every asset. This simplifies firewall management. You can whitelist specific IP ranges, allowing seamless two-way communication while blocking all unauthorized external pings. If you’re looking to streamline this process, Choice IoT provides the infrastructure to deploy these static assignments at scale.
Private APN in the 5G and RedCap Era
As we move into 2026, 5G RedCap (Reduced Capability) is becoming the standard for medium-speed industrial applications. These devices require the low latency of 5G without the high cost of full-scale modules. A private apn for iot is the perfect companion for RedCap deployments. While network slicing offers logical traffic separation, a private APN provides physical gateway isolation. They are complementary technologies. Slicing prioritizes your traffic, while the APN secures it. This combination future-proofs your deployment, ensuring your infrastructure is ready for the next generation of industrial automation and mobile AI workloads.

Strategic Implementation: Best Practices for Solution Providers
For VARs and integrators, the deployment phase is where profitability meets technical reality. Manual configuration is a scalability killer. Pre-configuration is the solution. Hardcode your private apn for iot at the factory level. This eliminates manual field errors and ensures every device is secure the moment it powers on. Speed to market increases. Operational friction disappears. It’s about building a repeatable, hardened process that doesn’t rely on technician expertise at the edge.
Maintaining a consistent security posture across multiple carriers is a common hurdle. You need carrier-agnostic security. By using a multi-carrier IoT SIM paired with a unified private gateway, you apply the same firewall rules and custom DNS settings regardless of the underlying network. Custom DNS adds an extra layer of protection by controlling address resolution. This prevents devices from being redirected to malicious servers. Couple this with traffic shaping. Prioritize critical telemetry data over non-essential firmware updates to ensure your most vital packets always have the right of way.
Choosing Between Shared and Dedicated Private APNs
Shared Private APNs offer a cost-effective entry point for small to mid-sized fleets. You get the isolation of a private tunnel without the overhead of a completely bespoke gateway. It’s security for the masses. As your deployment scales into the thousands, move to a Dedicated Private APN. This provides total customizability. You control the IP ranges, routing protocols, and authentication methods. It’s enterprise-grade infrastructure built for total operational autonomy. Building a robust foundation now ensures your scalable iot connectivity solutions can grow alongside your fleet without introducing new vulnerabilities or management complexity.
Operational Efficiency and Cost Management
Efficiency drives your bottom line. Traditional on-device VPN clients drain battery life and consume precious CPU cycles. A private apn for iot handles encryption at the network level, removing the need for heavy software on the device. This extends hardware longevity. You can further lower data consumption through header compression and direct routing. Use real time iot device monitoring to validate performance and catch anomalies before they impact your billing cycle. If you’re ready to simplify your multi-carrier strategy, partner with Choice IoT to deploy a private network that scales with your business.
Centralized Control: Managing Private APNs with CAMP™
A private apn for iot is only as effective as the platform managing it. Many providers treat the APN as a passive barrier. We treat it as an active operational engine. Through the CAMP™ platform, security becomes a visible, manageable asset. You get unified visibility. Monitor every byte of traffic across your entire fleet from a single dashboard. Identify unauthorized access attempts the moment they occur. Intelligent alerts notify you of unusual patterns, allowing for immediate intervention before a breach or data overage impacts your bottom line. A thorough iot connectivity platform comparison consistently shows that most dashboards reveal problems without providing the tools to resolve them remotely.
Connectivity issues typically require expensive truck rolls. CAMP™ eliminates this friction. Use the Remote Network Reset feature to cycle connections from your desk. It’s efficient. It’s cost-effective. Complement this with SIM Lock security. This ensures your SIMs only function within your designated Private APN. If a SIM is removed and placed in a consumer device, it becomes useless. This provides total perimeter protection that extends from the network core to the physical hardware.
Total Operational Control with Choice IoT
Provisioning shouldn’t be a bottleneck for growth. CAMP™ simplifies the entire Private APN lifecycle for VARs and integrators. Automate security rules to prevent bill shock. If a device exceeds its data threshold, the platform acts automatically to protect your margins. Real-time diagnostics allow you to troubleshoot secure tunnels in seconds, not hours. You don’t have to guess. You see the live state of every connection. This level of transparency removes the logistical stress of managing large-scale deployments.
Next Steps for Your Secure Deployment
Ready to scale your infrastructure? Integrating your private apn for iot with multi carrier iot sim cards provides the global reach your enterprise requires. It’s about combining localized security with international flexibility. Consult with our experts to design a custom APN architecture that fits your specific security and routing needs. Don’t leave your edge exposed to the public web. Secure your IoT edge-contact Choice IoT today for a Private APN consultation.
Securing Your Path to Scalable IoT Success
The transition from public internet reliance to private network architecture is no longer a luxury; it’s a strategic necessity for the 2026 landscape. By implementing a private apn for iot, you eliminate the vulnerabilities of the open web while gaining absolute control over your data pathways. You’ve seen how this architecture supports M2M communication with static IPs and simplifies complex multi-carrier deployments through centralized management. The risks of “shadow IoT” and data breaches are too high to ignore. Your infrastructure deserves a foundation built on isolation, transparency, and high performance.
Choice IoT provides the tools to make this transition seamless. Our CAMP™ platform offers real-time visibility into every connection. You’ll reduce operational costs with features like Remote Network Reset and benefit from our extensive Carrier Device Certification support. Don’t wait for a security breach to force your hand. Take control of your perimeter today and build a deployment that is as resilient as it is scalable. Your hardware is ready for the next generation of connectivity. We’re here to help you bridge the gap.
Get a Private APN Consultation with Choice IoT
Frequently Asked Questions
What is the primary benefit of a Private APN for IoT?
The primary benefit is total isolation from the public internet. By creating a dedicated gateway, your devices remain invisible to external scanners and automated bots. This architecture eliminates the largest attack surface in cellular connectivity. It ensures that data only moves between your hardware and your private infrastructure. You gain peace of mind and operational integrity through a hardened, invisible perimeter.
Do I need a VPN if I am already using a Private APN?
In most cases, a VPN client on the device is redundant. A private apn for iot establishes a secure tunnel at the network level. This removes the processing burden from your hardware and simplifies your software stack. While you might use a VPN to connect your data center to the carrier gateway, the device-to-gateway link is already hardened and encrypted without needing extra on-device clients.
Can a Private APN support static IP addresses for my devices?
Yes, supporting static IP addresses is a fundamental feature of this architecture. Static IPs allow for reliable two-way communication and simplified firewall management. You don’t have to deal with the chaos of rotating dynamic addresses. This is critical for industrial M2M applications where reaching a specific device remotely is a daily requirement for polling, diagnostics, or firmware updates.
How does a Private APN improve IoT battery life?
It improves battery life by reducing computational overhead. Traditional security methods like on-device VPNs drain power through constant encryption and handshaking. Because a private apn for iot handles security at the network layer, your device module doesn’t have to run heavy encryption software. This efficiency extends the operational life of battery-powered sensors and remote assets by minimizing power-hungry processing cycles.
Is a Private APN compatible with all cellular carriers?
Compatibility depends on your connectivity provider. While individual carriers offer their own APNs, a multi-carrier solution ensures consistent security across different networks. This approach prevents vendor lock-in. You maintain the same security rules and routing protocols whether your device is connected to a tier-one carrier in the US or a local provider abroad; all managed through a single, unified gateway.
What happens if a SIM card is removed from a device using a Private APN?
Security remains intact through SIM Lock features. If a SIM is stolen or moved to an unauthorized device, it will fail to connect to the private gateway. The CAMP™ platform can also trigger an immediate alert for any unauthorized hardware changes. This ensures that your private pathway is never compromised by physical tampering or attempts to use your data plan on secondary devices.